Business areas
We protect your systems, data and reputation against increasingly sophisticated threats. Assessment, defence and 24/7 monitoring come together in one integrated service.
- 24/7
- SOC monitoring
- 180+
- security specialists
- 15 min
- response commitment for critical incidents
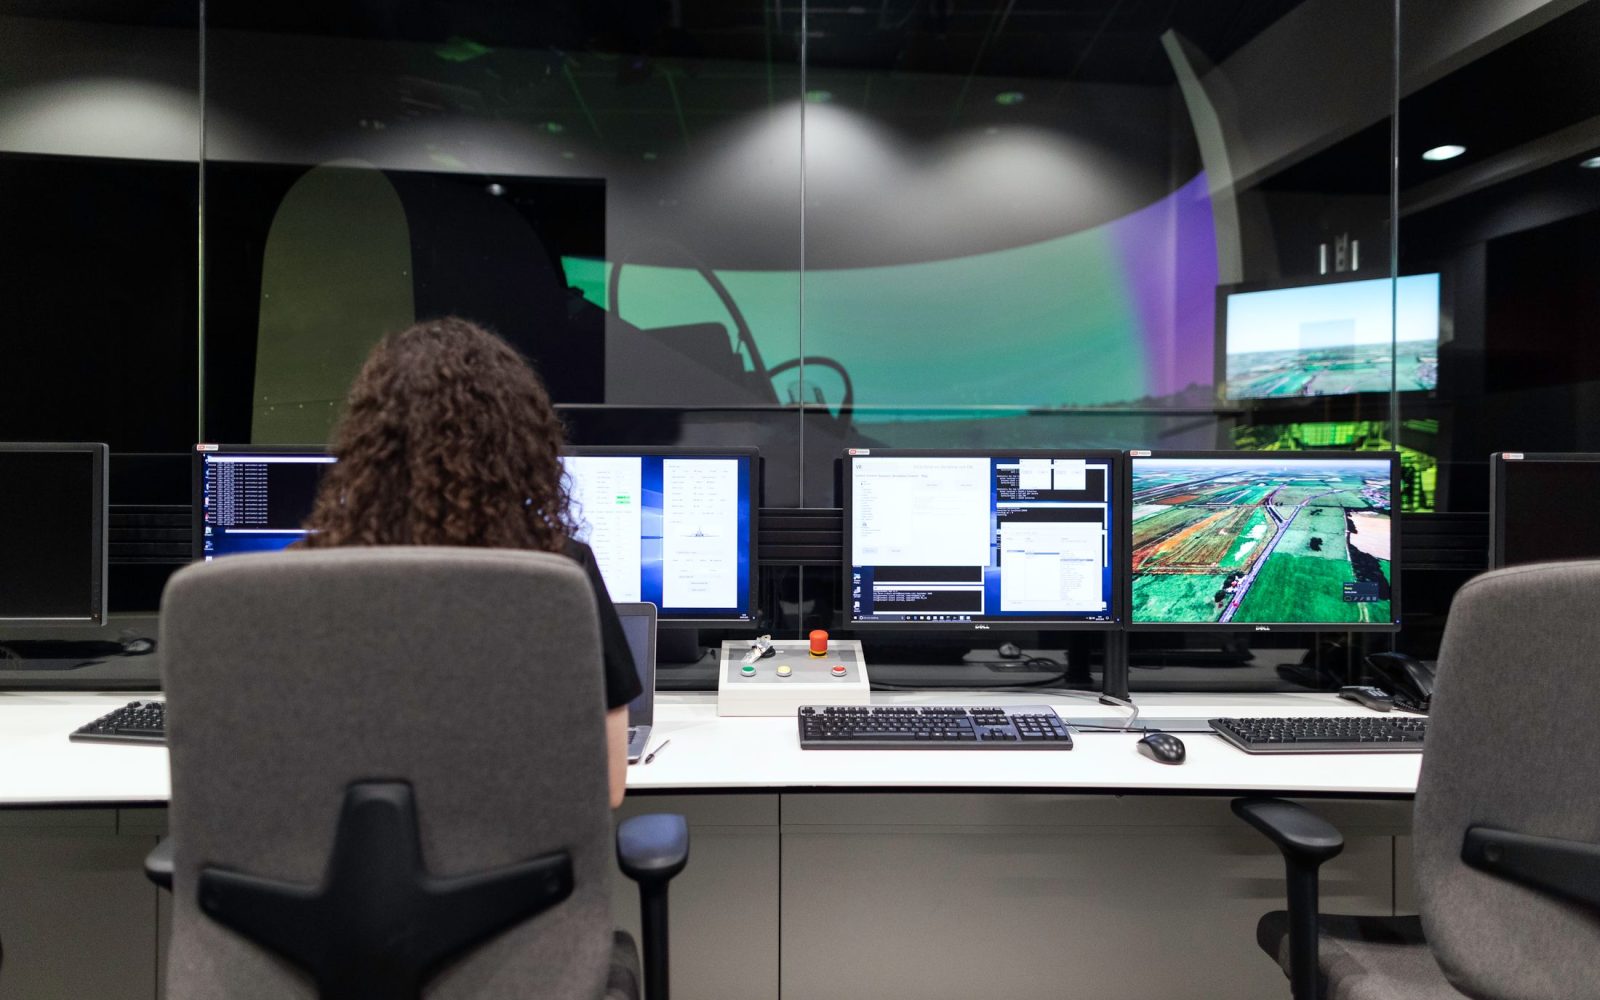
Cybersecurity is no longer just an IT concern; it is a business risk that boards now track directly. Zentrova's 180-plus security specialists help organisations understand which risks they actually face, put the right defences in place and respond quickly when incidents happen. Our security operations centres in Hanoi and Da Nang run around the clock, every day of the year. We work with banks, insurers, hospitals, manufacturers and public bodies, many of which hold large volumes of personal and financial data.
Core capabilities
- Managed SOC services: continuous monitoring, detection and incident response.
- Penetration testing of web and mobile applications, APIs and infrastructure, plus targeted red team exercises.
- Compliance assessment and advisory for ISO 27001, PCI DSS and national information system security regulations.
- Cloud security: configuration reviews, identity management and privileged access control.
- Secure software development: code reviews and automated vulnerability scanning built into CI/CD pipelines.
- Incident response and digital forensics, available even if you are not yet a regular client, with a hotline staffed around the clock.
Technology & methods
- SIEM, SOAR and EDR, integrated and tuned to each client's environment.
- Threat intelligence focused on attack groups targeting Southeast Asia.
- Zero Trust principles: multi-factor authentication, network segmentation and least-privilege access.
- Detection coverage mapped against common attack techniques to expose blind spots.
- Security awareness programmes and phishing simulations for employees at every level, from front-line staff to the board.
Our process
- Assess risk — identify critical assets, relevant threats and gaps in protection.
- Plan the roadmap — prioritise measures by risk level and available budget.
- Deploy defences — configure tools, policies and response procedures, then verify that they work as intended.
- Monitor 24/7 — three tiers of analysts triage and handle alerts continuously.
- Test and improve — regular attack simulations and quarterly reporting to leadership.
No system is ever perfectly secure, but every organisation can detect threats sooner and recover faster. Zentrova helps you get there with measurable commitments on time to detect and time to respond, written into every service agreement. Each month you receive a plain-language report showing what was detected, what was stopped and what should be strengthened next, so leadership can see exactly where security spending is going.